PHP Security Flaw: Nepalese Government Websites Temporarily Shut Down

22nd October 2026, Kathmandu
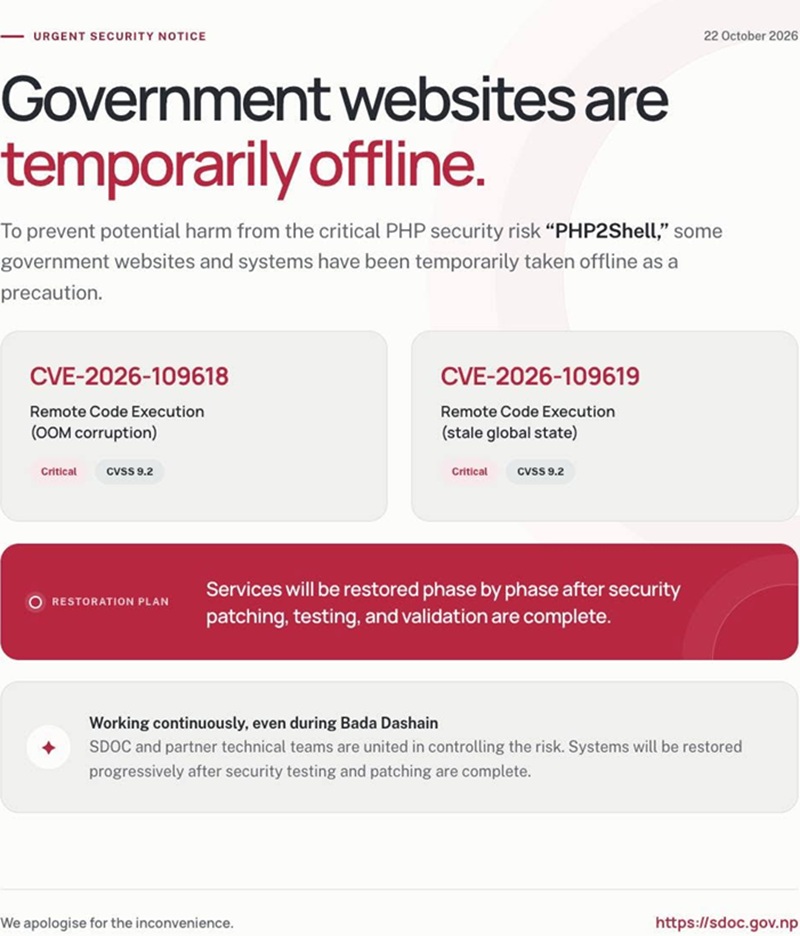
High-severity PHP@Shell vulnerability (CVSS 9.2) prompts SDOC to temporarily suspend several Nepalese government websites to prevent cyberattacks.
Several Nepalese government websites and online portals have been temporarily taken offline following the discovery of a critical cybersecurity vulnerability in PHP software worldwide.
The Software Development and Operation Center (SDOC) issued an urgent security notice confirming that proactive measures were taken to prevent potential cyberattacks, data breaches, and unauthorized server access.
Critical ‘PHP@Shell’ Vulnerability Detected
According to the SDOC, the disruption stems from a high-severity flaw known as PHP@Shell (tracked under CVE-2026-109618 and CVE-2026-109619). Carrying a Common Vulnerability Scoring System (CVSS) rating of 9.2 out of 10, this critical bug affects PHP-based systems globally.
Advertisement

The flaw allows unauthorized malicious actors or hackers to execute arbitrary code directly on target servers without logging in, enabling them to gain complete remote control over vulnerable systems.

Technical Response and Restoration Efforts
Despite the ongoing Dashain festival holidays, technical teams from the SDOC and associated cybersecurity units are working continuously to contain the threat and update system infrastructures.
Authorities are currently applying necessary security patches and conducting rigorous system testing. The center clarified that government websites and digital public services will be restored gradually once security assessments confirm the systems are fully secured.
The SDOC has expressed regret for the inconvenience caused to citizens and users due to the sudden interruption of online services.
For more: PHP Security Flaw Nepalese Government